SUPPLIER MANAGEMENT
AI-powered supplier risk assessment, live in days not months.
Run supplier risk assessment and third party risk management in one place: assess, score and keep an eye on every supplier and vendor over time, with evidence documents, risk scoring and follow-up handled for you.
ALIGNED TO
NIS2
DORA
GDPR and ISO 27001 coming soon
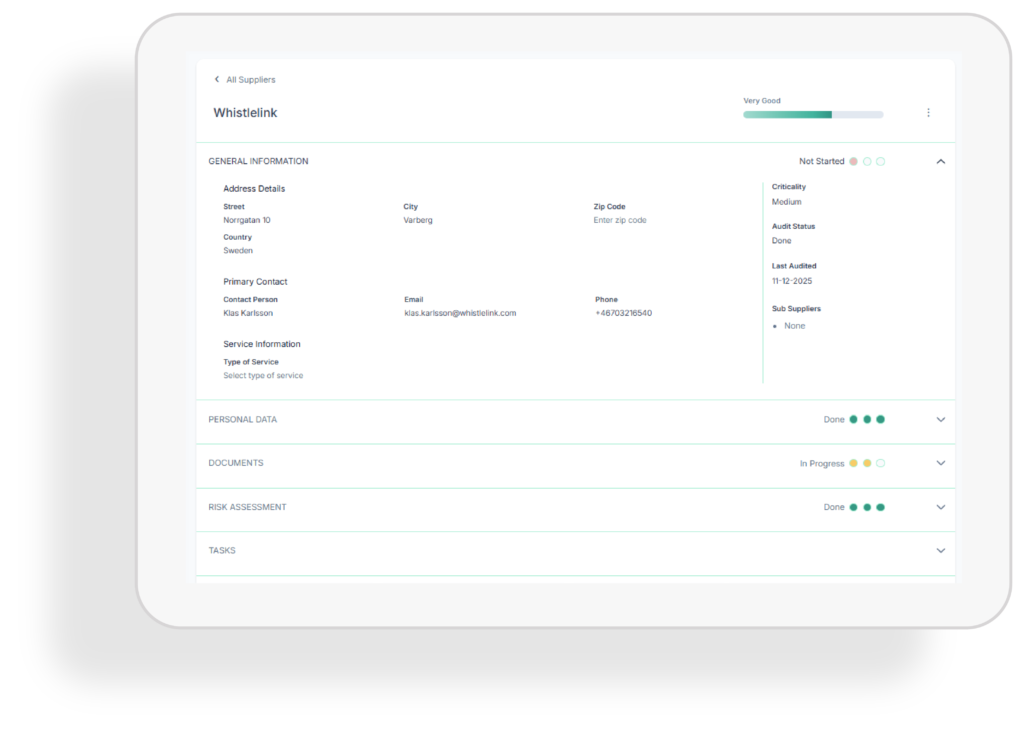
From manual vetting to audit-ready in weeks, not months. Here is how it runs in Trustlinks.
01
Map your suppliers
Bring every supplier and vendor into one register with contract details, category and a named owner for each relationship.
02
Assess and collect evidence
Run risk assessments for each supplier and upload certificates, policies and reports straight to their record.
03
Keep it up to date
Track expiring documents, planned reassessments and score changes, with findings feeding the same risk register.
AI THAT DOES THE FIRST DRAFT
You don't start from a blank page
Knowing which risks a supplier actually brings, and what to do about them, is often the difficult part. Trustlinks gives you a starting point for both.
01
Suggested supplier risks
AI proposes the third-party risks that typically apply to a supplier like this one, based on what they deliver and how critical they are to you, so the first assessment starts from a working draft.
02
Recommended mitigations and follow-up
For each supplier you get suggested controls and follow-up actions to consider, with the reasoning shown, so deciding what to do next takes minutes rather than workshops. Findings and actions feed the same risk register, not a separate tool.
Suggestions only. Nothing enters your supplier record or your risk register until someone on your team reviews and approves it.
PLATFORM CAPABILITIES
The whole supplier lifecycle in one place
Supplier and vendor management from one register: onboard, assess, score and keep every third party up to date, with evidence documents stored on each supplier record, so nothing gets lost in email threads.
Supplier register
One place for every third party, with criticality, category, contract details and risk score. Ownership is clear, so nothing falls between teams.
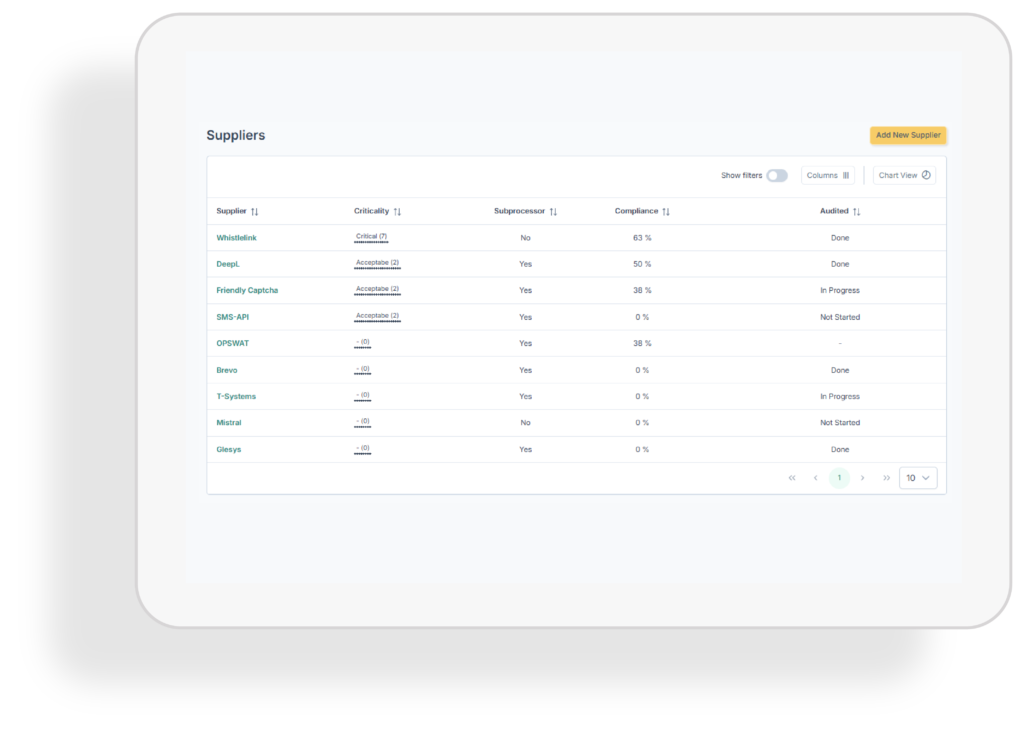
Risk assessment for every supplier
Assess each supplier against the risks they bring, from security and continuity to sustainability. The findings land in the same risk register as the rest of your risk management, so supplier exposure sits next to everything else you track.
Risk scoring and tiering
Score suppliers the same way every time and group them by criticality, so the deep assessments go to the third parties that actually matter.
Upload documentation as evidence
Upload certificates, policies, audit reports and contracts straight to each supplier record. Everything is versioned, easy to find and tied to the assessment it supports.
Kept up to date
Reassessment dates and certificate expiry dates stay visible on each supplier record, so you can see what needs a fresh look and assessment isn’t a once-a-year exercise.
Framework alignment
Supply chain requirements in NIS2 and DORA are covered from the same assessment, with GDPR coming soon and ISO 27001 to follow. You can also use supplier management on its own for other standards and certifications you work under.
"With Trustlinks we've gained complete oversight of risks and suppliers, allowing us to act before issues escalate, and strengthening trust across our organisation."
Cecilia Axéll Ryttergaard
CEO, Travel Support Europe
Why choose Trustlinks for supplier management
Supplier risk management usually fails on follow-up, not on intent. Trustlinks takes away the chasing, the version control and the manual merge, so assessment actually get finished.
Built for teams without a risk function
You don’t need a dedicated vendor risk team. Assessment, scoring and follow-up are set up for you, so you just work through the list.
A working assessment in days, not months
This solves one urgent job rather then starting an org-wide overhaul. Import your suppliers and the first assessments can go out the same week.
No more certificates buried in email
Every document you receive from a supplier is uploaded to that supplier record, so the current version is always the one your team finds.
Ask what you need, keep it in one register
You can ask suppliers about anything that matters to you, from security and continuity to sustainability topics, and the answers feed the same organisational risk register, so you see exposure in one view instead of two tools.
ALREADY HAVE A SUPPLIER LIST
Import your suppliers and contracts, group them by criticality, and start assessments the same week.
STARTING FROM SCRATCH
Use a suggested tiering model and the AI risk suggestions to get your most critical suppliers assessed straight away.
HOW IT WORKS
From supplier list to steady oversight in four steps
A repeatable cycle that keeps supplier, vendor and third party risk management current between audits, not just during them.
01
Start with your suppliers
Bring in your supplier list with contract and category details and set an owner for each relationship, then start assessing right away.
02
Group by criticality
Sort suppliers so the depth of each assessment matches the real exposure, and your team's effort goes where it counts.
03
Assess and upload evidence
Run the risk assessment for each supplier and upload their certificates, policies and reports as evidence, with the status of every supplier visible in one view.
04
Keep it up to date
Keep track of expiring documents, planned reassessments and score changes, and report on your supply chain whenever you're asked.
PRICING
From 99 EUR per month
Supplier management is available as a standalone subscription, so you don’t have to commit to the full platform to get started. The price scales with the number of employees, and onboarding is included.
The prices shown are examples. You always get an individual quote based on what you actually need.
- Supplier risk management module with risk assessments, automated risk scoring and evidence collection
- Clear visibility of your high risk suppliers
- Unlimited users, so procurement and security can work in the same place
- Guided onboarding and support in your language
NOT READY TO TALK?
Run a free supplier scan
See how exposed your supply chain is today. A short assessment shows which supplier relationships need attention first. No commitment and no sales call.
Vendor risk is one part of the bigger picture
Trustlinks connects supplier findings to your organisational risk register, so security, continuity and compliance exposure all sit in a single view.
LET'S GET IN TOUCH!Want us to tell you more?
Find out how Trustlinks can support your organisation. You simply choose when, and we’ll explain the why’s and how’s!
FAQ
Supplier risk assessment questions
Common questions about supplier risk management, vendor management and third party risk management under NIS2 and DORA.
What is supplier risk assessment?
Supplier risk assessment or management is how you judge and keep track of the risk a third party brings into your organisation, covering security, continuity, compliance and sustainability, and then keep an eye on it for as long as the relationship lasts. It includes onboarding checks, risk assessment, evidence collection, scoring and regular reassessment.
Is supplier management the same as vendor management or third party risk management?
In practice, yes. Vendor management, supplier risk management and third party risk management describe the same work: knowing who you depend on, how much risk each relationship carries, and what you’re doing about it. Trustlinks covers all of it in one register, whether your team calls them suppliers, vendors or partners.
How many suppliers should we assess?
Not all of them to the same depth. Group suppliers by criticality: the critical ones get full assessments and regular reassessment, while low-impact vendors get a lighter check.
How do we document what a supplier has told us?
You upload their certificates, policies, audit reports and contracts to the supplier record as evidence, and link them to the risk assessment they support. Everyone on your team sees the current version, and expiry dates are tracked so you know when to ask again.
Can we buy supplier management on its own?
Yes. Supplier management works as a standalone module from 99 EUR per month, with the price scaling by number of employees. You can add other parts of the platform later without moving your data. Pricing on the site is an example, so you always get an individual quote based on what you actually need.
How does this support NIS2 and DORA supply chain requirements?
Both regulations expect documented oversight of third parties, including assessment, contractual controls and ongoing monitoring. Trustlinks maps supplier assessments to those requirements and keeps the trail of assessment dates, evidence documents and follow-up ready for a regulator or auditor.
Can we collect sustainability data too?
Yes. You decide what to ask each supplier, so sustainability topics can sit in the same assessment as security and continuity and your teams work from one set of supplier data instead of two.